primedefence

Our job is to tell you the truth about your security and your AI.

Primedefence is an independent assessor. We measure how mature your security operations and your AI really are against recognized standards, we help you choose and hold MSSP and MDR providers to account from the buyer's side, and we help you design the SOC team that closes the gap. No SOC to run for you and nothing riding on the result of an assessment. In Spanish and English, ready for your board and your regulator.

Our story.

Primedefence began in 2021 from a single conviction: security is best judged from the outside, with no stake in the result. In 2023 we consolidated as a firm with one focus, assessing maturity with rigor and independence, and delivering evidence a board can defend.

We started with the SOC-CMM because maturity should be measured, not guessed, against a recognized standard, the same way every time. From there the work grew with our clients: AI maturity against the EU AI Act and ISO/IEC 42001, buyer-side selection and oversight of MSSP and MDR providers, and the design of the SOC teams and hiring plans that make everything else work.

Today Primedefence operates internationally, with clients across several continents. Same methodology, same executive register, in Spanish and English: an independent read that travels across regulatory frameworks and geographies without losing rigor.
Professionals in suits talking in a modern meeting room
An executive in a suit reviewing a report in an office

We assess. We never sell what we assess.

An assessment is only worth as much as its independence. We do not run your SOC, and when we help you select an MSSP or MDR provider we never bid for the contract ourselves. Private inference implementation is a separately scoped service and is not presented as an independent assessment of our own work. There is no second agenda behind the recommendation.

Every finding is traced to evidence: interviews, configuration, telemetry, runbooks, not opinion or vendor preference. And every report is written twice over, once for the engineers who have to act on it, once for the board and regulator who have to sign it. Native Spanish and English, not a translation layer.

Who leads the work

A team with an operational track record in SOC, CSIRT and threat analysis. Both take part in every assessment: one leads and signs, the other reviews the technical evidence.

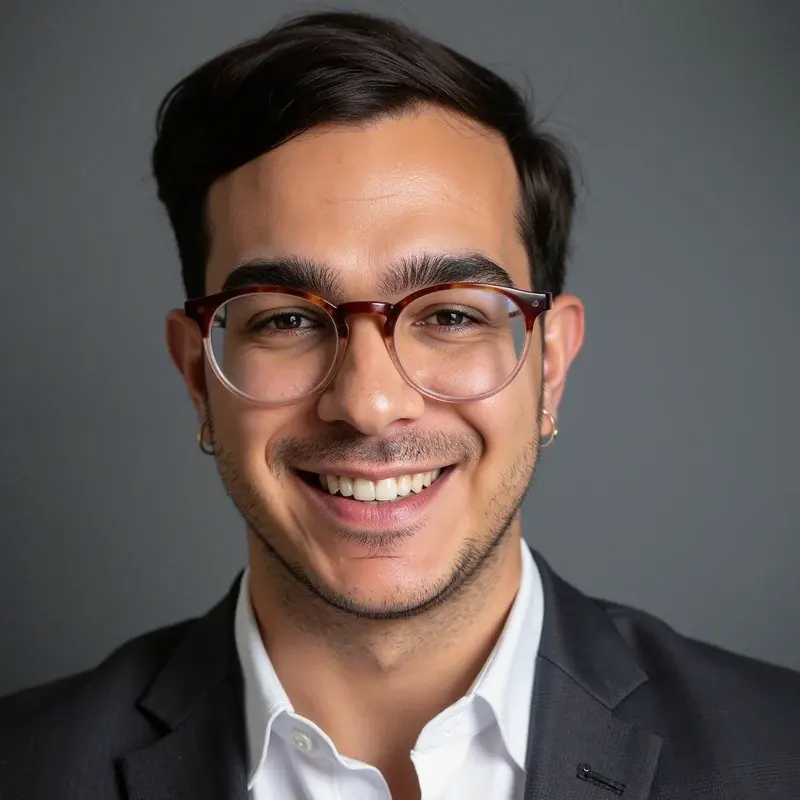
Daute Delgado

Daute Delgado

CEO & Co-founder, Primedefence

Daute Delgado is CEO and co-founder of Primedefence. He spent more than a decade defending airlines, managed SOCs and international organizations, first as an operator and later leading security teams.

  • Associate C|CISO
  • Silver Winner, Cyber Security Excellence Awards 2021
  • 10+ years in security operations
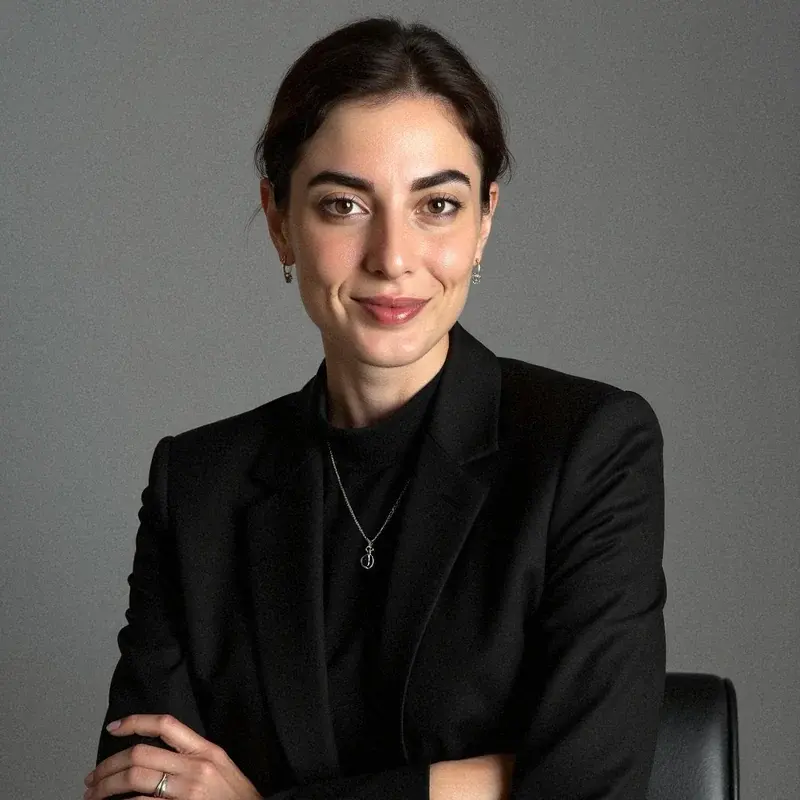
Annalisa Battistelli

Annalisa Battistelli

CTO at Primedefence

Annalisa Battistelli is CTO of Primedefence. She graduated in Cybersecurity from Sapienza Università di Roma and went straight into operations: first as a Threat Analyst in the Malwarebytes Research Team, then in CSIRT operations for international organizations.

  • Cybersecurity, Sapienza Università di Roma
  • Former Threat Analyst, Malwarebytes Research
  • CSIRT operations for international organizations
A professional presenting findings to a committee in a boardroom

Our values.

Five principles we hold on every engagement, whether it is a SOC-CMM assessment, an AI maturity read, a provider selection or a team design. They are the reasons our work reads differently from a vendor pitch.

No stake in the result of an assessment. We assess, advise and help you choose; we never operate your SOC or bid for it. The recommendation answers to your interest, not ours.